Compeas Auditor Tool
A shared workspace for external auditors and the organisations they audit — live compliance data on one side, evidence requests answered on the other.
See the Auditor Tool at work
Each company’s controls, evidence and risks are read straight from its GRC and compared across frameworks, with audit samples, evidence requests and a findings report.
Read the transcript
Audit firms and large groups both depend on evidence from many companies. Too often it arrives as spreadsheets, screenshots and email attachments, in a different shape every time.
The Compeas Auditor Tool connects to each company’s Compeas GRC. Each company issues an access key that expires, and decides what it shares. Controls, evidence, policies and risks are then read as they are, not as a copy.
Every company is on one dashboard: what needs attention, which incidents are open, and which evidence requests are still waiting.
The frameworks view compares companies across ISO 27001, NIS2, GDPR, SOC 2 and NIST CSF 2.0, down to each requirement, including the NIS2 rules of each company’s own country.
For companies that make connected devices or software, the Cyber Resilience Act is covered too: each product’s class and proof and, where the company shares them, how its vulnerabilities are fixed and reported.
Audit periods, populations and samples are drawn in the tool, and every result is signed by name. Evidence requests and comments go straight into each company’s GRC, and the answers come back.
Findings, observations and review coverage come together in the findings report, ready to print or save as PDF. Every account signs in with two-factor authentication, and every view is recorded in the audit trail.
Less time chasing evidence. More time on the audit itself.
Compeas. Compliance Made Easy.
One audit, seen from both sides
The auditor’s view and the audited organisation’s view of the same audit.
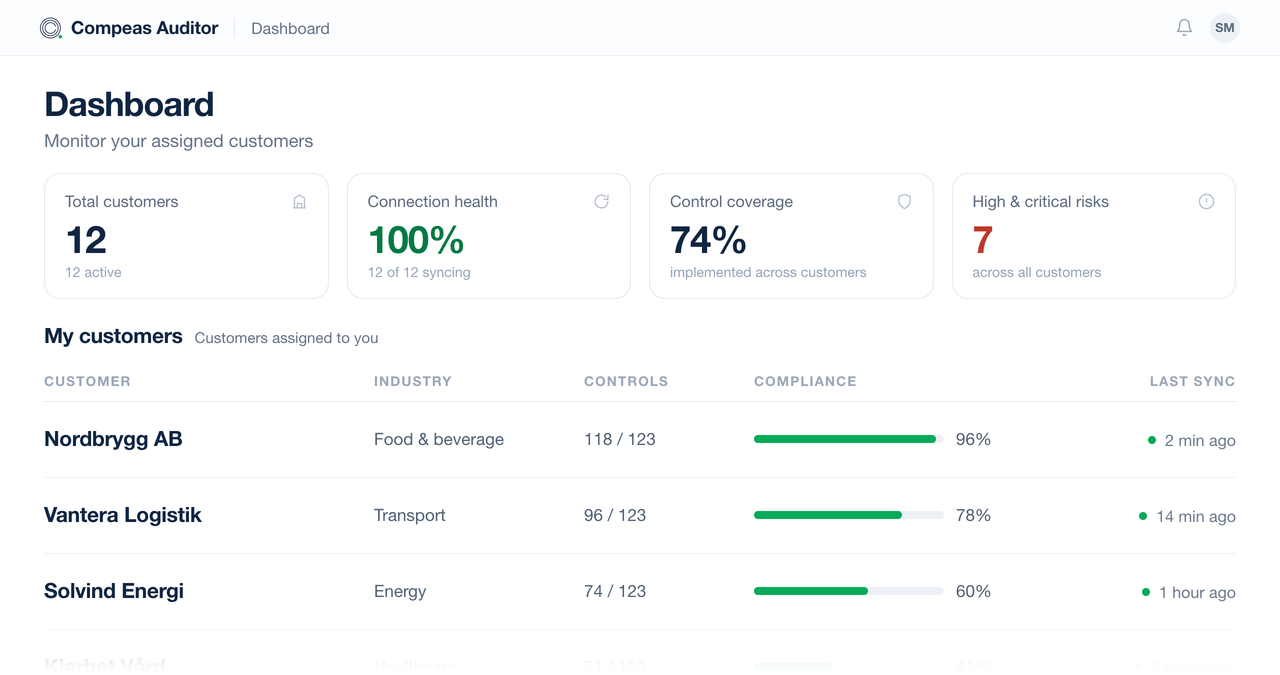
Every customer’s posture on one screen
Assigned customers, their control coverage and open risks, read straight from each customer’s Compeas GRC. Audit planning starts from current data instead of a document request.
- An auditor’s own customers, a colleague’s or the whole firm’s
- Connection health and last sync for each customer
- Control coverage and high-risk counts across the portfolio
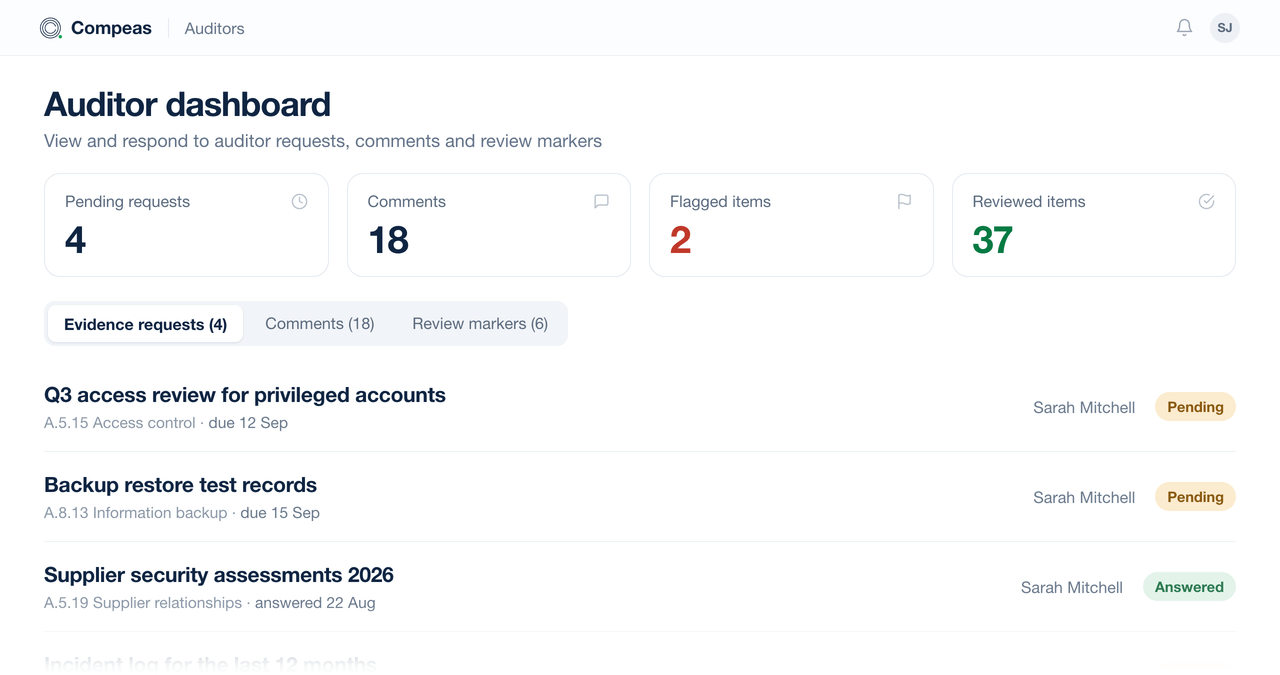
Evidence requests answered where the evidence lives
The auditor raises a request against a specific control. The organisation answers it in Compeas GRC, next to the policy and evidence it refers to, without email threads or shared drives.
- Requests, comments and review markers in one queue
- Each request tied to the control it tests
- A full trail of what was asked, answered and reviewed
Key capabilities
For audit firms, internal audit and group compliance teams
Evidence at the source
Evidence is read directly from each company’s Compeas GRC, without email threads or file shares.
Current status
Each company’s controls, evidence, risks and incidents as of the latest sync, with the time of that sync shown.
Shared audit work
Evidence requests and comments go straight into each company’s GRC, and every audit result is signed by name.
Findings report
Findings, observations and review coverage in one report, ready to print or save as PDF.
Firm-wide oversight
One dashboard for an auditor’s own customers, a colleague’s or the whole firm’s portfolio.
Connection and sync
Each company connects its GRC with an access key that expires, and the data syncs on its own. Connection health and last sync are shown for each customer.
Incidents across companies
How each company handles its incidents: reports filed on time and decisions taken within 24 hours. Full incident records are shared only when the company chooses.
Products under the CRA
Each company’s product register for the Cyber Resilience Act: class, support period and proof for each product. Vulnerabilities are shared only when the company chooses.
The whole group in one view
Each company runs its own Compeas GRC and decides what it shares, through access keys that expire. The Auditor Tool gives the group one view across all of them.
Read the transcript
A group with many companies has many compliance programmes: different systems, different countries, different rules.
Keeping them aligned with spreadsheets and status meetings does not scale.
With Compeas, every company runs its own Compeas GRC. It connects to the company’s directory and systems, tests its controls automatically every day, and keeps the evidence, policies, risks and incidents its audits need. Each company works to its own frameworks, including the NIS2 rules of its own country, and its data stays its own.
The same platform runs in every company, so the whole group works the same way.
At group level, the Compeas Auditor Tool brings them together. It connects to each company’s GRC and reads its compliance posture live: frameworks, controls, evidence, risks and incidents. The group’s CISO and internal audit see where every company stands, which frameworks fall behind, and what needs attention first.
Work flows both ways. Evidence requests, comments and audit samples go out to the companies, and their answers come straight back.
Each company decides what it shares, through access keys that expire.
The whole group in one view. Every company still in control.
Compeas. Compliance Made Easy.
Ready to bring every audit into one view?
Book a walkthrough to see how audit firms and groups follow compliance across many companies in one tool.